Buy cyberfenua.eu ?
We are moving the project
cyberfenua.eu .
Are you interested in purchasing the domain
cyberfenua.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy cyberfenua.eu ?
How to reach servers behind an OpenVPN network?
To reach servers behind an OpenVPN network, you need to first establish a connection to the OpenVPN server using a VPN client. Once connected, you can access the servers behind the OpenVPN network by using their internal IP addresses. Make sure that the routing and firewall rules on the OpenVPN server allow traffic to reach the servers behind the network. Additionally, ensure that the servers behind the OpenVPN network are configured to accept incoming connections from the VPN subnet. **
How to access servers behind an OpenVPN network?
To access servers behind an OpenVPN network, you first need to connect to the OpenVPN server using a VPN client. Once connected, you will be assigned an IP address within the OpenVPN network. You can then access the servers behind the OpenVPN network by using their internal IP addresses or hostnames. Make sure that the necessary firewall rules and routing configurations are in place to allow traffic to flow between your device and the servers behind the OpenVPN network. **

Similar search terms for Openvpn
Top-Angebote
Products related to Openvpn:
-
DrayTek Vigor 2927 Wired Dual-WAN VPN Firewall RouterEnterprise-class desktop router with integrated 6-port Gigabit Ethernet switch and dual WAN ports. Supports up to 50 concurrent VPN tunnels and 25 SSL VPN tunnels with 60,000 NAT sessions capacity. Advanced routing protocols include BGP, static IPv4/IPv6, and policy-based routing with comprehensive remote management options.283,49 £*Shipping: 0,00 £Secure redirect to the provider
-
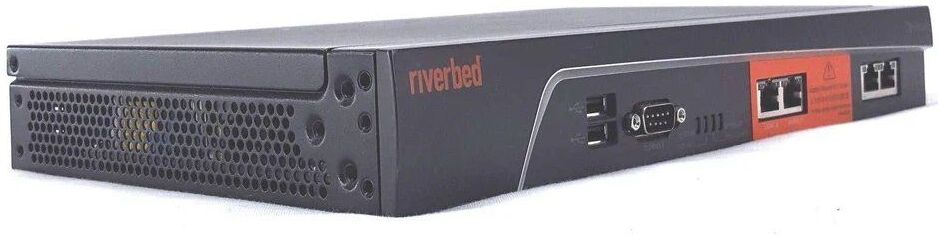
Riverbed Steelhead 250 Series Firewall SHA-00250-M, NewStep into enterprise network optimisation with the Riverbed Steelhead 250 Series (SHA-00250-M), a compact WAN acceleration appliance designed to improve application performance and reduce bandwidth usage across distributed networks. Built for branch offices and small-to-medium environments, it enhances data transfer speeds and user experience over WAN connections. ✔️ WAN Optimisation Technology – Accelerates applications and data transfer across wide-area networks for faster performance ✔️ Bandwidth Reduction (Up to 60–95%) – Minimises network traffic using data deduplication and compression ✔️ Application Acceleration – Improves performance for file sharing, email, web apps, and databases ✔️ 24/7 Enterprise Operation – Designed for continuous use in business environments ✔️ Compact Desktop Form Factor – Space-saving design suitable for branch offices and IT racks ✔️ Optimised TCP/UDP Handling – Enhances network efficiency and reduces latency ✔️ Integrated Bypass Ports – Maintains network availability even during power loss or failure ✔️ Low Power Consumption (~40W) – Efficient operation for always-on deployments ✔️ Supports Multiple Users & Sites – Scales for multi-branch connectivity and enterprise setups ✔️ Easy Deployment – Works without major changes to existing infrastructure or applications The Riverbed Steelhead 250 Series is designed for businesses that need faster application performance over WAN without upgrading bandwidth . Whether you're running remote offices, centralising servers, or improving cloud access, this appliance delivers proven optimisation and efficiency. Ideal for enterprise IT environments, it keeps your network fast, efficient, and cost-effective .63,99 £*Shipping: 0,00 £Secure redirect to the provider
-
DrayTek Vigor 2962 Dual-WAN 2.5Gb Ethernet Firewall VPN RouterEnterprise-grade router with dual WAN ports supporting 200 concurrent VPN tunnels and 300,000 NAT sessions. Supports multiple routing protocols (BGP, OSPF, RIP) and VoIP standards (SIP, H.323) with integrated 4-port Gigabit/2.5 Gigabit switch. Desktop or rack-mountable form factor with comprehensive remote management capabilities via HTTP, HTTPS, SSH, SNMP, and TR-069.546,99 £*Shipping: 0,00 £Secure redirect to the provider
-
DrayTek Vigor 2927ax Dual-WAN Wi-Fi 6 VPN Firewall RouterEnterprise-grade Wi-Fi 6 router with dual gigabit WAN ports and integrated 6-port switch supporting up to 60,000 NAT sessions. Handles 50 concurrent VPN tunnels and 25 SSL VPN connections with support for advanced routing protocols including BGP and policy-based routing. Desktop form factor with 2-year warranty.361,99 £*Shipping: 0,00 £Secure redirect to the provider



-
Is OpenVPN good?
Yes, OpenVPN is considered to be a good option for secure and private internet connections. It is an open-source VPN protocol that is widely used for its strong encryption and flexibility. OpenVPN is known for its ability to provide a high level of security and privacy, making it a popular choice for individuals and businesses looking to protect their online activities. Additionally, OpenVPN is compatible with a wide range of operating systems and devices, making it a versatile and reliable option for VPN users. **
-
Why is the OpenVPN connection not working?
The OpenVPN connection may not be working due to several reasons such as incorrect configuration settings, firewall blocking the connection, server issues, or network connectivity problems. It is important to check the configuration settings to ensure they are accurate, verify that the firewall is not blocking the connection, and troubleshoot any network connectivity issues. Additionally, checking the server status and logs can help identify any server-side issues causing the connection problem. **
-
How do I remove an OpenVPN profile?
To remove an OpenVPN profile, you can simply delete the configuration file associated with that profile from your OpenVPN client's configuration directory. This directory is typically located in the "config" folder within the OpenVPN installation directory. Once you have located the configuration file for the profile you want to remove, you can simply delete it from the "config" folder. After deleting the configuration file, you may need to restart your OpenVPN client for the changes to take effect. **
-
Does Pi-hole block requests only over OpenVPN and not in the home network?
Pi-hole can block requests both over OpenVPN and in the home network. When set up correctly, Pi-hole can be used to block ads, trackers, and malicious websites on all devices connected to the network, regardless of whether they are connected through OpenVPN or directly in the home network. This provides consistent protection and privacy for all devices using the network. **
Does Pi-hole block requests only through OpenVPN and not in the home network?
Pi-hole can block requests on both OpenVPN and the home network. When Pi-hole is set up on a network, it acts as a DNS sinkhole, blocking unwanted requests at the DNS level regardless of where the request originates from. This means that Pi-hole can block requests on any device connected to the network, whether it is through OpenVPN or within the home network. **
How can I access my local network through an OpenVPN server on my QNAP?
To access your local network through an OpenVPN server on your QNAP, you will first need to set up the OpenVPN server on your QNAP device. Once the server is set up, you will need to configure the OpenVPN client on your computer or mobile device to connect to the QNAP's OpenVPN server. You will then be able to access your local network as if you were physically connected to it, allowing you to access files, printers, and other resources on your local network remotely. Make sure to follow the specific instructions provided by QNAP for setting up the OpenVPN server and client to ensure a secure and successful connection. **
Top-Angebote
Products related to Openvpn:
-
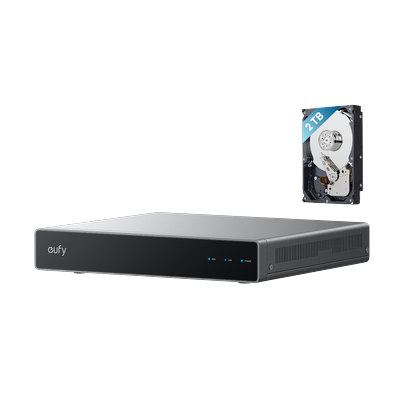
eufy Network Video Recorder S4 for Home Security CamerasLocal AI Agent: Unlock proactive, real-time security with our local AI agent, fueled by 6T/8-Core power for instant analysis, genuine threat identification, and decisive action. Customize no-go zones and alerts, enabling AI to accurately detect real...599,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Axis A9801 Security Relay for Network Video Door StationsThe Axis A9801 Security Relay adds a secure lock-control relay for doors managed by Axis network video door stations such as the A8004-VE and A8105-VE, so the door strike is not wired directly to the outdoor unit. It supports 12 V and 24 V door strikes, has tamper control and fits in a standard installation box. Plastic housing.179,49 £*Shipping: 0,00 £Secure redirect to the provider
-
DrayTek Vigor 2927 Wired Dual-WAN VPN Firewall RouterEnterprise-class desktop router with integrated 6-port Gigabit Ethernet switch and dual WAN ports. Supports up to 50 concurrent VPN tunnels and 25 SSL VPN tunnels with 60,000 NAT sessions capacity. Advanced routing protocols include BGP, static IPv4/IPv6, and policy-based routing with comprehensive remote management options.283,49 £*Shipping: 0,00 £Secure redirect to the provider
-
Riverbed Steelhead 250 Series Firewall SHA-00250-M, NewStep into enterprise network optimisation with the Riverbed Steelhead 250 Series (SHA-00250-M), a compact WAN acceleration appliance designed to improve application performance and reduce bandwidth usage across distributed networks. Built for branch offices and small-to-medium environments, it enhances data transfer speeds and user experience over WAN connections. ✔️ WAN Optimisation Technology – Accelerates applications and data transfer across wide-area networks for faster performance ✔️ Bandwidth Reduction (Up to 60–95%) – Minimises network traffic using data deduplication and compression ✔️ Application Acceleration – Improves performance for file sharing, email, web apps, and databases ✔️ 24/7 Enterprise Operation – Designed for continuous use in business environments ✔️ Compact Desktop Form Factor – Space-saving design suitable for branch offices and IT racks ✔️ Optimised TCP/UDP Handling – Enhances network efficiency and reduces latency ✔️ Integrated Bypass Ports – Maintains network availability even during power loss or failure ✔️ Low Power Consumption (~40W) – Efficient operation for always-on deployments ✔️ Supports Multiple Users & Sites – Scales for multi-branch connectivity and enterprise setups ✔️ Easy Deployment – Works without major changes to existing infrastructure or applications The Riverbed Steelhead 250 Series is designed for businesses that need faster application performance over WAN without upgrading bandwidth . Whether you're running remote offices, centralising servers, or improving cloud access, this appliance delivers proven optimisation and efficiency. Ideal for enterprise IT environments, it keeps your network fast, efficient, and cost-effective .63,99 £*Shipping: 0,00 £Secure redirect to the provider
-
How to reach servers behind an OpenVPN network?
To reach servers behind an OpenVPN network, you need to first establish a connection to the OpenVPN server using a VPN client. Once connected, you can access the servers behind the OpenVPN network by using their internal IP addresses. Make sure that the routing and firewall rules on the OpenVPN server allow traffic to reach the servers behind the network. Additionally, ensure that the servers behind the OpenVPN network are configured to accept incoming connections from the VPN subnet. **
-
How to access servers behind an OpenVPN network?
To access servers behind an OpenVPN network, you first need to connect to the OpenVPN server using a VPN client. Once connected, you will be assigned an IP address within the OpenVPN network. You can then access the servers behind the OpenVPN network by using their internal IP addresses or hostnames. Make sure that the necessary firewall rules and routing configurations are in place to allow traffic to flow between your device and the servers behind the OpenVPN network. **
-
Is OpenVPN good?
Yes, OpenVPN is considered to be a good option for secure and private internet connections. It is an open-source VPN protocol that is widely used for its strong encryption and flexibility. OpenVPN is known for its ability to provide a high level of security and privacy, making it a popular choice for individuals and businesses looking to protect their online activities. Additionally, OpenVPN is compatible with a wide range of operating systems and devices, making it a versatile and reliable option for VPN users. **
-
Why is the OpenVPN connection not working?
The OpenVPN connection may not be working due to several reasons such as incorrect configuration settings, firewall blocking the connection, server issues, or network connectivity problems. It is important to check the configuration settings to ensure they are accurate, verify that the firewall is not blocking the connection, and troubleshoot any network connectivity issues. Additionally, checking the server status and logs can help identify any server-side issues causing the connection problem. **
Similar search terms for Openvpn
-
DrayTek Vigor 2962 Dual-WAN 2.5Gb Ethernet Firewall VPN RouterEnterprise-grade router with dual WAN ports supporting 200 concurrent VPN tunnels and 300,000 NAT sessions. Supports multiple routing protocols (BGP, OSPF, RIP) and VoIP standards (SIP, H.323) with integrated 4-port Gigabit/2.5 Gigabit switch. Desktop or rack-mountable form factor with comprehensive remote management capabilities via HTTP, HTTPS, SSH, SNMP, and TR-069.546,99 £*Shipping: 0,00 £Secure redirect to the provider
-
DrayTek Vigor 2927ax Dual-WAN Wi-Fi 6 VPN Firewall RouterEnterprise-grade Wi-Fi 6 router with dual gigabit WAN ports and integrated 6-port switch supporting up to 60,000 NAT sessions. Handles 50 concurrent VPN tunnels and 25 SSL VPN connections with support for advanced routing protocols including BGP and policy-based routing. Desktop form factor with 2-year warranty.361,99 £*Shipping: 0,00 £Secure redirect to the provider
-
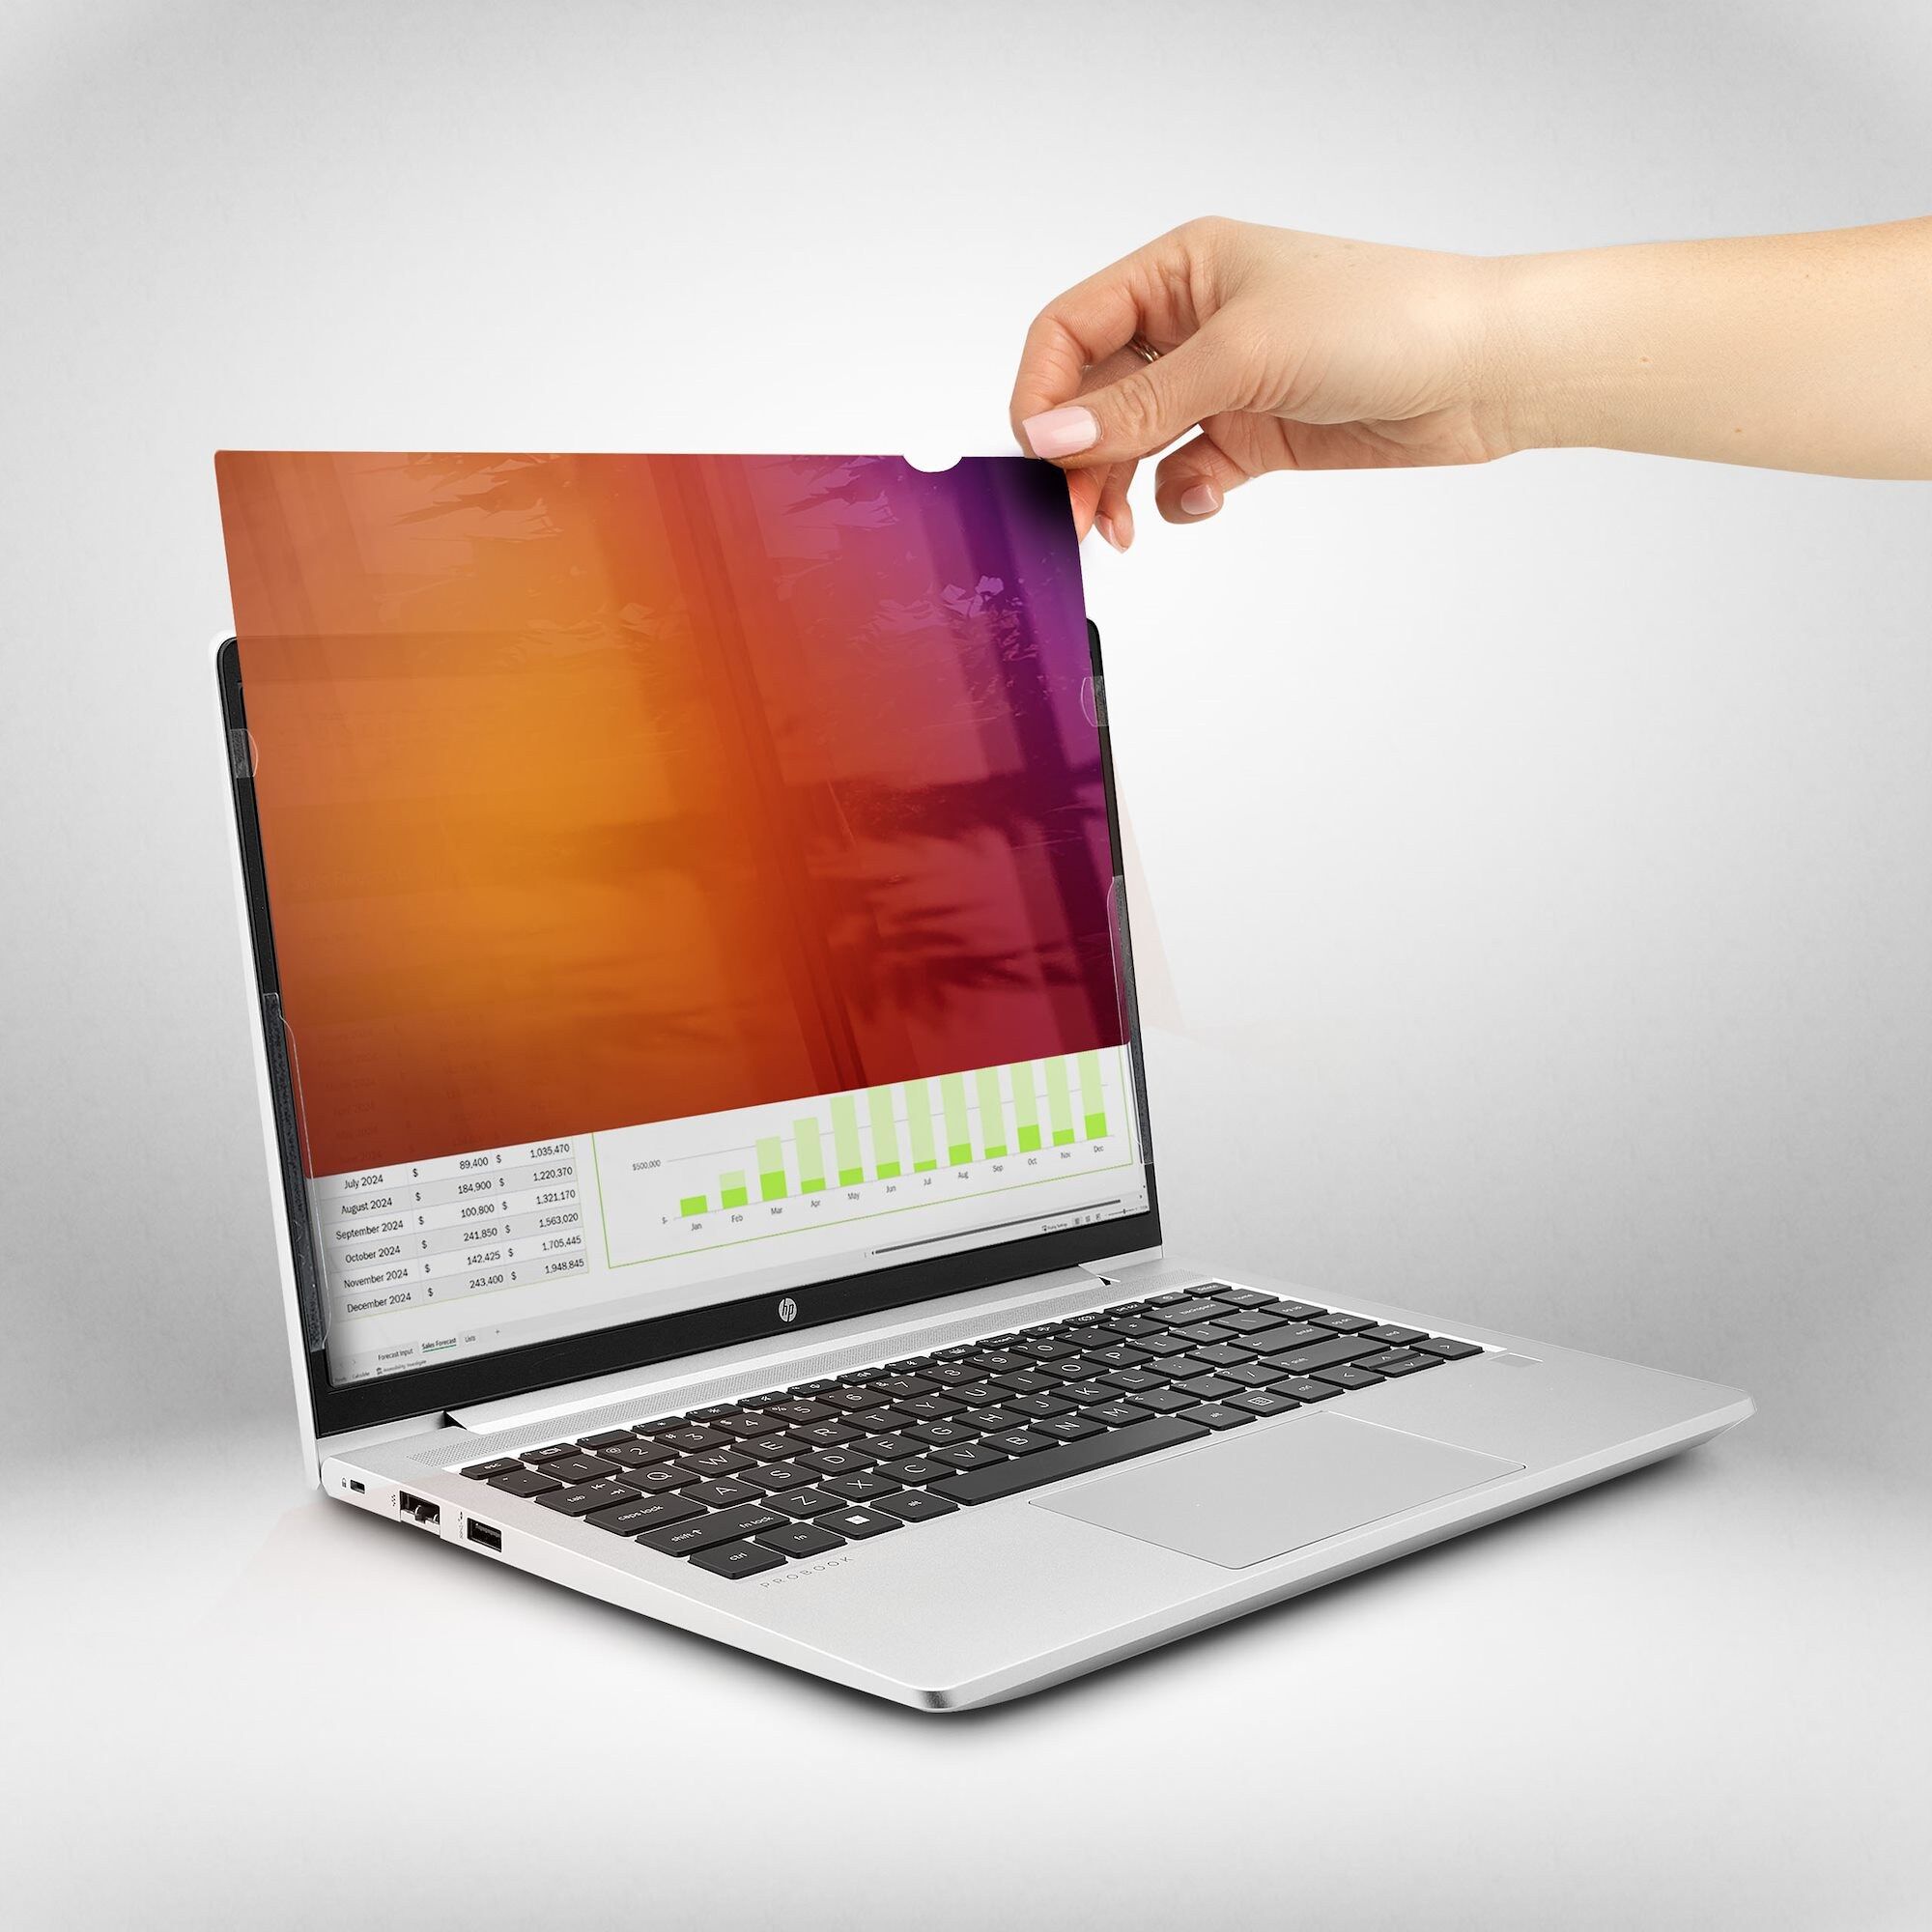
StarTech.com 14-inch 16:9 Laptop Privacy Screen, Reversible Gold Filter w/Enhanced Privacy, Computer Security Filter, Removable Screen Protector/ShielPrevent visual eavesdropping by limiting the viewing angle of your laptop screenThis Laptop Privacy Screen features a universal design compatible with 14-inch laptop screens with a 16:9 aspect ratio display. Gold Privacy Filters have a reflective surface that instantly transitions from a clear view to a mirror effect outside of the intended viewing angle, significantly improving visual privacy when working in an office or public environment.Prevent Visual EavesdroppingThe gold security filter is a convenient solution that features a quick shift to a mirror-like effect to protect confidential data from unwanted viewers while maintaining a clear view of 60 degrees (+/- 30 degrees from the center) for the user.Reversible FilterThe privacy filter's removable and reversible design allows users to effortlessly switch between a glossy gold side for maximum privacy and an anti-glare matte side for environments prone to glare. The matte side provides additional screen protection with a scratch- and fingerprint-resistant coating.Hassle-free InstallationThe universal design won't interfere with top-mounted webcams, sensors, or when closing the lid. The privacy filter can be installed in two different ways. Affix the privacy shield to bezel-less displays using the transparent and residue-free adhesive strips. Alternatively, use the slide mount tabs to install the privacy screen on displays with bezels. The latter is recommended when frequent reversal or removal is required.Blue Light ReductionReduce eye strain and improve visual comfort with this blue light-reducing privacy shield. It blocks 40% - 51% of the blue light emitted from the display in the 380nm - 480nm wavelength range. Digital eye strain can lead to symptoms like headaches, dry eyes, and blurred vision.The StarTech.com Advantage48,99 £*Shipping: 0,00 £Secure redirect to the provider
-
How do I remove an OpenVPN profile?
To remove an OpenVPN profile, you can simply delete the configuration file associated with that profile from your OpenVPN client's configuration directory. This directory is typically located in the "config" folder within the OpenVPN installation directory. Once you have located the configuration file for the profile you want to remove, you can simply delete it from the "config" folder. After deleting the configuration file, you may need to restart your OpenVPN client for the changes to take effect. **
-
Does Pi-hole block requests only over OpenVPN and not in the home network?
Pi-hole can block requests both over OpenVPN and in the home network. When set up correctly, Pi-hole can be used to block ads, trackers, and malicious websites on all devices connected to the network, regardless of whether they are connected through OpenVPN or directly in the home network. This provides consistent protection and privacy for all devices using the network. **
-
Does Pi-hole block requests only through OpenVPN and not in the home network?
Pi-hole can block requests on both OpenVPN and the home network. When Pi-hole is set up on a network, it acts as a DNS sinkhole, blocking unwanted requests at the DNS level regardless of where the request originates from. This means that Pi-hole can block requests on any device connected to the network, whether it is through OpenVPN or within the home network. **
-
How can I access my local network through an OpenVPN server on my QNAP?
To access your local network through an OpenVPN server on your QNAP, you will first need to set up the OpenVPN server on your QNAP device. Once the server is set up, you will need to configure the OpenVPN client on your computer or mobile device to connect to the QNAP's OpenVPN server. You will then be able to access your local network as if you were physically connected to it, allowing you to access files, printers, and other resources on your local network remotely. Make sure to follow the specific instructions provided by QNAP for setting up the OpenVPN server and client to ensure a secure and successful connection. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.